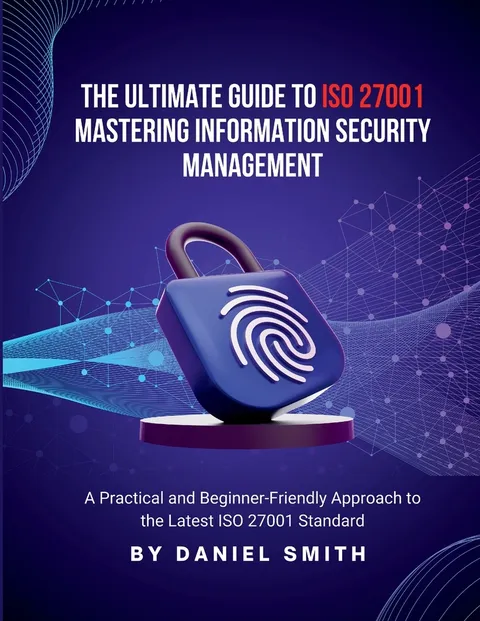
The Ultimate Guide to ISO 27001
A Practical and Beginner-Friendly Approach to the Latest ISO 27001 Standard
Report an issue
Tell us what's wrong and we'll take a look.
Thanks – we got it. We'll review and follow up if needed.
The Ultimate Guide to ISO 27001: Mastering Information Security Management
A Practical and Beginner-Friendly Approach to the Latest ISO 27001 Standard
OverviewThis book provides a practical roadmap for understanding and implementing ISO 27001, the leading international standard for information security management. Written in simple, direct language, it offers real-world application rather than just theory.
Learn how to create an Information Security Management System (ISMS), protect critical information, meet customer and regulatory expectations, and prepare for audits confidently. The goal is not just certification but building a security function that supports the business, fosters trust, and continually improves.
Who This Book Is ForThis book is for:
- Small and mid-size businesses needing security but lacking a full security team
- Compliance and audit teams preparing for ISO 27001 certification
- Founders, managers, and executives demonstrating data protection to customers
- New security officers and IT leads seeking a clear starting point
- Students and professionals building skills in governance, risk, and compliance (GRC)
No prior ISO knowledge is required. This book starts from the basics.
What You Will Learn- The Core of ISO 27001
- Understand the structure and expectations of ISO 27001 certification.
- How to Build an ISMS
- Step-by-step guidance on defining scope, setting policies, assigning responsibilities, and documenting evidence.
- Risk Management in Plain Language
- Learn to identify security risks, evaluate impacts, choose treatments, and defend decisions to auditors and management.
- Annex A Security Controls
- Clear explanations of control areas such as access control, asset management, incident response, and supplier security.
- Support, Awareness, and Culture
- Train people, communicate expectations, and integrate security into normal work practices rather than as a checklist exercise.
- Internal Audits and Continuous Improvement
- Plan and conduct internal audits, measure performance with KPIs, and use findings for continuous improvement.
ISO 27001 provides a defensible, recognized way to prove responsible information management. It helps build trust in sales conversations, reduces legal exposure, and ensures proper data handling.
ISO 27001 is increasingly becoming a requirement, especially in sectors like technology, healthcare, finance, telecom, e-commerce, and service delivery.
How This Book Is StructuredEach chapter follows a practical flow:
- Concept explained simply
- Real business relevance
- Actionable steps you can implement
- Immediate use examples, templates, or checkpoints
- Beginner-friendly language
- Actionable steps applicable to your environment
- Focus on real risks rather than theoretical scenarios
- Clear links between security and business value
- Designed for small teams, not just large enterprises
This book helps you build a repeatable system that not only passes audits but also protects the organization, proves control, and fosters ongoing improvement.
Daniel Smith
Daniel Smith is a psychotherapist and the author of Muses, Madmen, and Prophets and Monkey Mind. His writing has appeared in The Atlantic, The New York Times Magazine, and The New Yorker, among other publications. He lives in Brooklyn, New York.
More by Daniel Smith
Why Readwise Books?
Readwise Books is an ebook & audiobook platform that automatically logs how much you and your friends read, making it fun and easy to read more. Learn more →